
Information Security and Privacy
Information Security/Cybersecurity Governance Framework
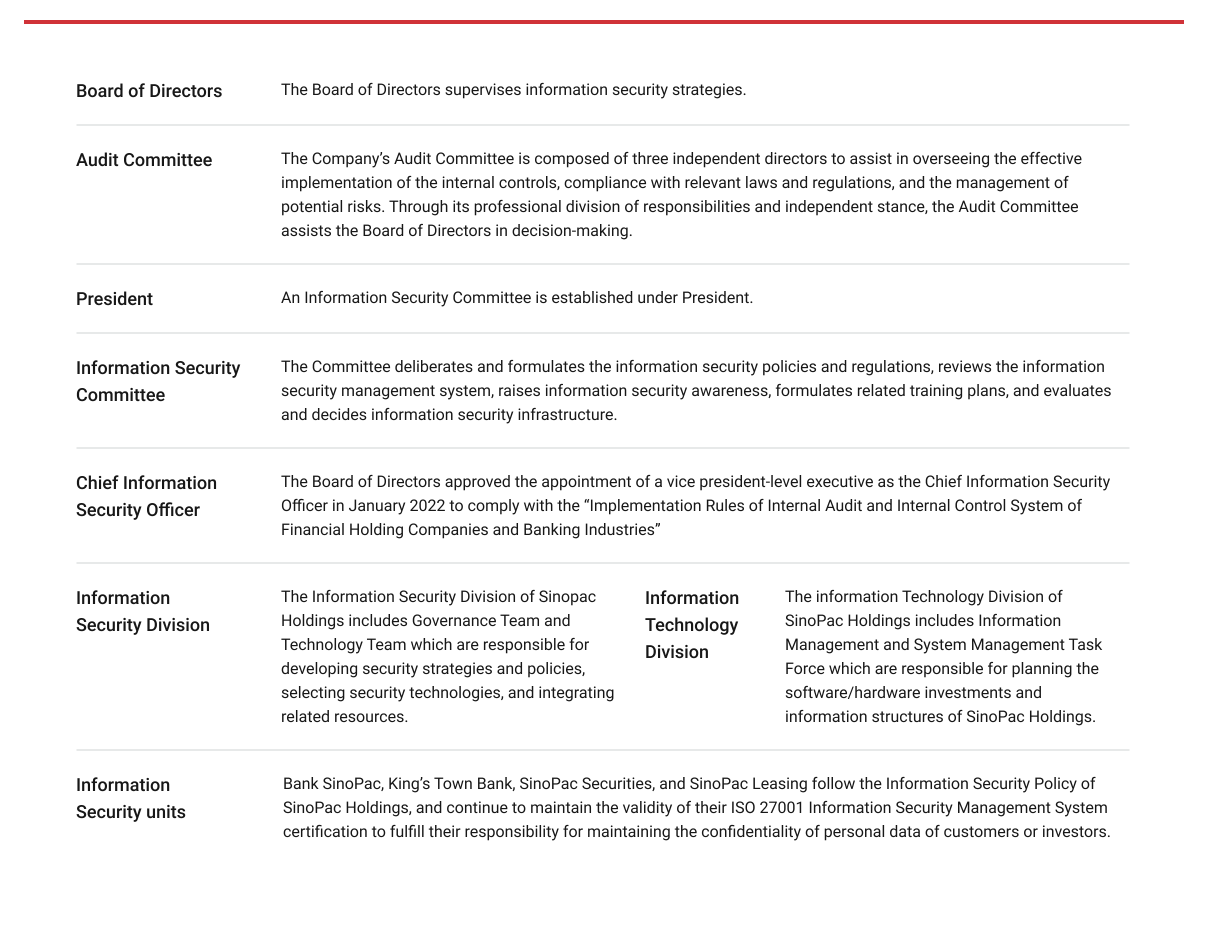
SinoPac Holdings has a comprehensive information and network security governance framework. The Board of Directors is the highest-ranking unit responsible for supervising the information security strategies of the Group. The Director Chi-Hsing YEH has expertise in information security and is responsible for overseeing the information security strategies of the Group. The Company set up the Information Security Committee as the highest-ranking unit for managing information security. The Company also has the Information Security Division and Information Technology Division which oversee the integration of policies, technologies, and resources for the information security of SinoPac Holdings and subsidiaries. The Information Security Division reports on the status of information security implementation to the Audit Committee and the Board of Directors on a semi-annual basis.
In addition, to comply with the Implementation Rules of the Internal Audit and Internal Control System of Financial Holding Companies and Banking Industries, the Boards of Directors of SinoPac Holdings, Bank SinoPac, SinoPac Securities, and King’s Town Bank approved the appointment of a Vice President-level executive as the Chief Information Security Officer (CISO). Bank SinoPac, SinoPac Securities, and King’s Town Bank included the overall annual information security implementation into the Internal Control System Statement, which is signed by the Chairman, President, Chief Auditor, Chief Information Security Officer, and Chief Compliance Officer of the head office of each company.
SinoPac Holdings' Information Security/Cybersecurity Governance Framework and Division of Authority and Responsibility
Information Security Risk and Vulnerability Assessment
To enhance the internal information security protection of SinoPac Holdings, the Group and its subsidiaries conduct regular evaluations of information security risks and vulnerabilities to identify potential information security threats within systems and internal controls. In 2025, SinoPac Holdings and its subsidiaries did not incur any fines or financial losses resulting from major information security incidents that cause damage to information systems or equipment.
SinoPac Holdings' Implementation Measures for Information Security Management
| Item | Frequency | Main contents |
|---|---|---|
| Review of daily information security inspection reports | Daily | Uncover potential information security incidents by reviewing the information security inspection reports to reduce threats and impact |
| Conduct a weekly report on impersonation detection of senior executives on Chinese-language social media | Weekly | Continuously monitor posts and comments in financial fraud discussion forums to identify any impersonation of senior executives. |
| Convene monthly meetings of the Information Security Intelligence Center | Monthly |
Review the monitoring and control measures of terminal hosts, accounts with special privileges, user actions, and threat hunting for analysis and discussions
Review the resolutions of the Information Security Intelligence Center and the implementation of measures such as information security monitoring points |
| Convene an information security meeting | Monthly | Review the Company and subsidiaries information security protection mechanisms and plans |
| Review vulnerability scan reports | Quarterly | Review web and host vulnerability scanning reports and track the progress of vulnerability rectification, and continuously track vulnerability to strengthen information security capacity |
| Review penetration test reports | Semi-annually | Execute penetration tests for web pages and SWIFT to track the progress of vulnerability rectification and strengthen information security capacity |
Information Security Incident Response Process

Professional Training Program
To strengthen internal information security, SinoPac Holdings conducts annual online information security training for all employees. The courses include fundamental information security concepts, trends in information security, social engineering methodology, promotion of internal regulations, and the cultivation of information security awareness. SinoPac Holdings has incorporated compliance with information security requirements into employees' performance evaluation.
Information security awareness training for SinoPac Holdings employees in 2025
| Subsidiary | Recipients | Results of training programs |
|---|---|---|
| Bank SinoPac | Dedicated information security personnel | The personnel completed at least 15 hours of professional information security or professional skills training in accordance with regulations and received 69 professional certificates and 171 certificates of attendance to optimize the competencies of dedicated information security personnel in 2025. |
| Regular employees | Personnel of the head office, local and foreign business units, IT units, financial custody units, and other managerial units completed at least three hours of information security training in accordance with regulations. The social engineering exercises were conducted after the training with a 98.92% passing rate. Employees who fail to pass the exercise shall receive additional training and tests to ensure they pass. | |
| SinoPac Securities | Dedicated information security personnel | The personnel completed at least 15 hours of professional information security training courses in accordance with the Criteria Governing Internal Control Systems of Securities Firms, passing the evaluation and received 19 professional certificates and 15 certificates of attendance in 2025. |
| Regular employees | Personnel who are users of the information systems completed at least 3 hours of information security training in accordance with the Criteria Governing Internal Control Systems of Securities Firms. The passing rate of social engineering exercises was 98.76%. Employees who fail to pass the exercise shall receive enhanced training and additional tests to ensure they pass. | |
| King’s Town Bank | Dedicated information security personnel | The personnel completed at least 15 hours of professional information security or professional skills training in accordance with regulations and received 5 professional certificates and 6 certificates of attendance to optimize the competencies of dedicated information security personnel in 2025. |
| Regular employees | Personnel of the head office, local and foreign business units, IT units, financial custody units, and other managerial units completed at least three hours of information security training in accordance with regulations. The social engineering exercises were conducted after the training with a 98.89% passing rate. Employees who fail to pass the exercise shall receive additional training and tests to ensure they pass. |
Information security vulnerability analysis
For servers, web application services, and network infrastructure, vulnerability identification, classification, and prioritization assessments are conducted. Through automated tools or manual inspections, security vulnerabilities that could potentially be exploited by attackers are identified within the systems and are categorized based on their severity, exploitability, and potential impact. The analysis results help the organization understand its current information security risks. The information security team provides relevant scan reports and professional remediation recommendations, enabling equipment owners to carry out necessary fixes. This process reduces information security risks, enhances the organization’s security protection capabilities and resilience, and ensures compliance with regulations and supervisory authority requirements.
Internal audits of the IT infrastructure and/or information security management systems
SinoPac Holdings and its subsidiaries, in addition to regularly implementing internal control mechanisms, conducting self-assessments of legal compliance, and performing self-audits, also have the audit units conduct regular and ad hoc audits of each unit’s implementation of information security measures.
Independent external audit of the IT infrastructure and/or information security management systems
Bank SinoPac, King’s Town Bank, SinoPac Securities, and SinoPac Leasing have established information security units in accordance with the Information Security Policy of SinoPac Holdings, and continuously maintain the validity of their ISO 27001 Information Security Management System certification to fulfill their responsibility for protecting the personal data of customers or investors.
Escalation process for employees to report incidents, vulnerabilities, or suspicious activities
SinoPac Holdings has established a clear reporting mechanism that requires employees to immediately report any information security incidents, vulnerabilities, or suspicious activities to the information security unit. The information security unit classifies and handles incidents based on their severity, escalating reports to senior management or regulatory authorities when necessary. The entire process is documented and tracked to ensure that risks are promptly identified and effectively managed.